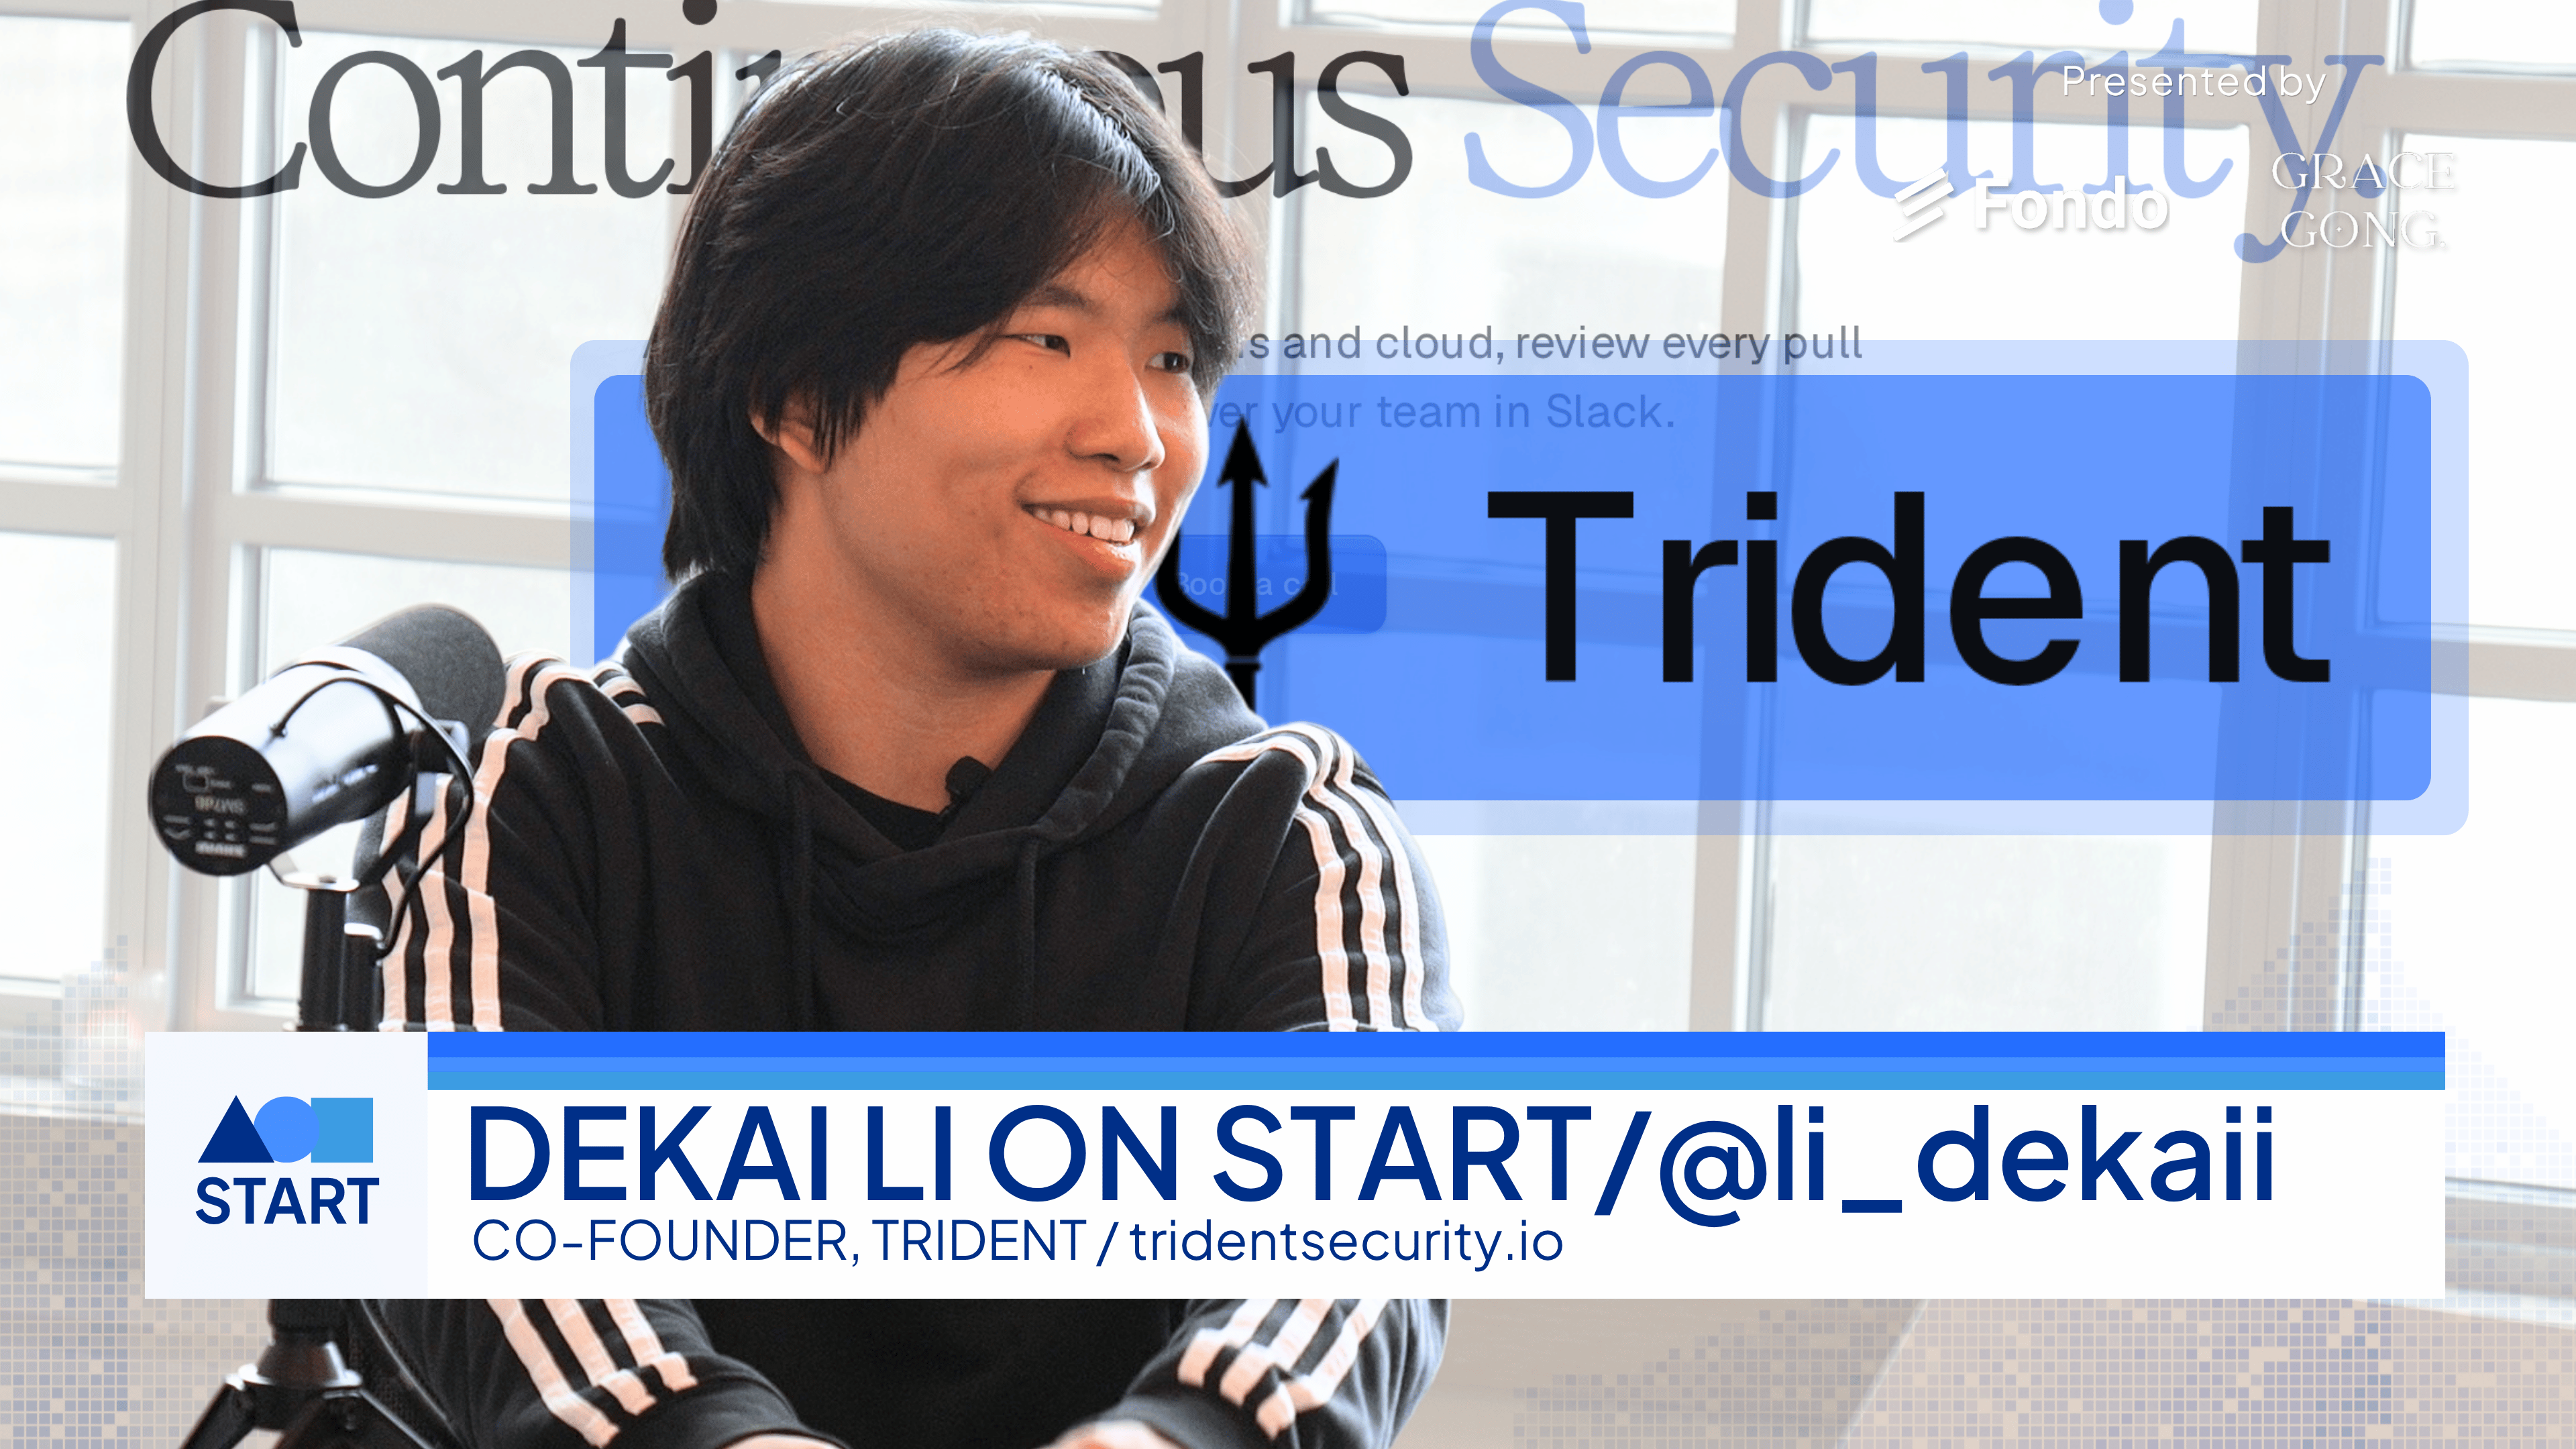
Shipping code got faster. Security has to keep up.
Before starting Trident, Dekai Li’s co-founder saw a workflow that concerned him:
A product manager supplied a project description. An engineer pasted it into a coding agent. The output became a pull request.
Dekai’s concern: manual pentesting couldn’t keep pace with how quickly developers were shipping.
That’s the problem they built Trident to address.
Trident uses AI to continuously pentest applications and APIs, review code, and identify security issues across cloud infrastructure.
But finding a possible vulnerability isn’t enough. You have to prove it’s real.
Dekai says validation is one of the hardest parts of AI pentesting.
That’s why Trident’s findings come with reproducible evidence, and fixes can be proposed as draft pull requests for engineers to review and merge.
The goal isn’t to give back the speed AI makes possible.
It’s to build security that can keep up with it.
Check out Trident "Continuous Security. AI agents test your apps, APIs and cloud, review every pull request, and answer your team in Slack."
🎙️Dekai Li Co-Founder & CTO, Trident on Fondo START w/ Guest Host, Grace Gong, Founder, Smart Venture Media
01:05 Why manual pentesting struggles to keep pace with development
02:12 Earning trust as young cybersecurity founders
03:25 Validating vulnerabilities and navigating AI guardrails
04:02 Building credibility through experienced hires and product results
05:18 A customer case: five critical vulnerabilities in 20 minutes
06:10 The founders’ cybersecurity backgrounds and path to Trident
07:02 How AI coding workflows helped inspire the company
08:13 Lessons from YC and building around customer feedback
09:32 Scanning software packages before they enter the codebase
10:21 Focusing on the security problems customers prioritize
Check out tridentsecurity.io
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Built for Delaware C-Corps. Trusted by 2,000+ startups.



Copyright © Fondo (BloomJoy, Inc.)